Google dismantles botnet secretly running on 1.3 million Android TV boxes
谷歌捣毁秘密运行在130万台安卓电视盒子上的僵尸网络
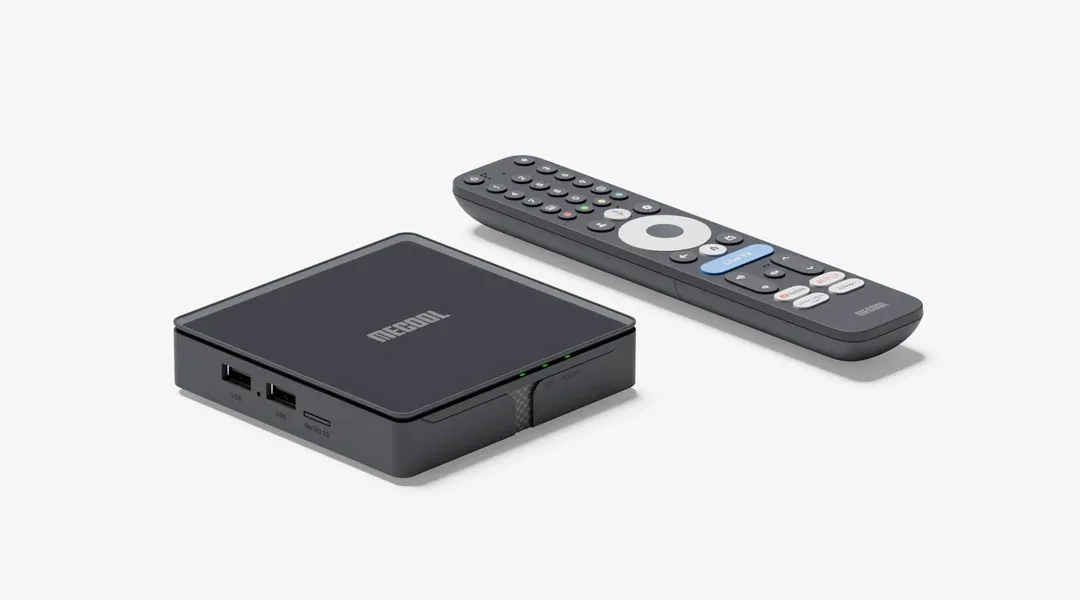
Google has cut ties with the company behind the botnet campaign.
谷歌称已关闭名为 x.cpe 的僵尸网络,其高峰期感染超过130万台经谷歌认证的安卓电视设备。恶意软件由深圳厂商 Videostrong 通过后门在设备联网后远程植入,绕过了认证筛查。
文章按时间线讲清一条攻击链:认证筛查为何失效、后门如何等设备联网再动手、stub 应用如何借系统权限装模块并关掉 Play Protect。读时可练因果链梳理与同义替换(如 evaded detection / missed the malware),并注意“认证—后门—权限”三层前提如何层层递进。适合练细节定位与技术类长句拆解。
Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says its screening process missed the malware due to "obfuscation techniques" employed by Shenzhen-based Videostrong Technology.
In a detailed blog post, the Threat Intelligence Group explains how the x.cpe botnet evolved quickly from a single-stage dropper into a modular three-stage malware platform that sold access to third parties. Manufacturers must have their devices certified if they want access to Google apps and branding, a process that is supposed to catch threats like this. However, Videostrong's compromised boxes, mostly sold under the MECOOL brand, evaded detection by using a backdoor to remotely install the malware after the devices were set up and online.
After devices appeared online, a stub application called x.cpe or com.oemservice would phone home. This package did not have any malicious capabilities of its own, but it had the system-level permissions necessary to install malware modules at the operator's behest. It also disabled Play Protect, which would have otherwise flagged the silently installed packages as malicious.
重点词汇
(8)
来源:Ars Technica · arstechnica.com